Cybersecurity Training
Hands-on cybersecurity training in Port Harcourt
2 or 3 months
Duration
Two levels
Foundation and Intermediate
Classes from 10am
Time depends on package
Certificate
Of completion
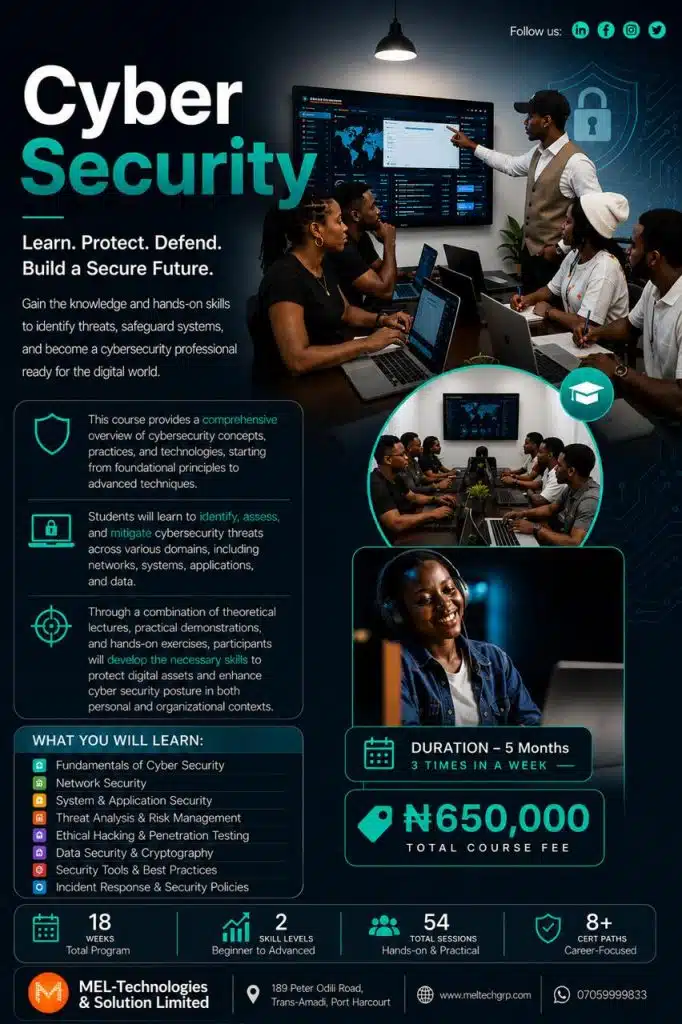
From ₦250,000
Intermediate (3 months): ₦400,000
- Live, instructor-led classes
- Practical exercises and projects
- Certified, experienced trainers
- Certificate of completion
Protect digital assets with practical skills.
Core security skills
- Network Security
- Endpoint Security
- Offensive Security (Ethical Hacking)
- Defensive Security (Blue Teaming)
- Incident Response and Digital Forensics
- Malware Analysis and Reverse Engineering
- Threat Intelligence and Cyber Threat Hunting
Hands-on ethical hacking
- Vulnerability Management
- System Auditing
- Application Auditing
- Social Engineering
- Open-Source Intelligence (OSINT)
Foundation modules.
Network Security
- Basics of Networking (IP, TCP/IP, DNS, Firewalls, VPNs)
- Common Network Threats (MITM, DDoS, Sniffing)
- Securing Networks with Firewalls & Intrusion Detection Systems (IDS)
- Hands-on: Setting Up a Basic Firewall and Packet Analysis with Wireshark
Endpoint Security
- Understanding Endpoints (Workstations, Mobile, IoT)
- Common Endpoint Threats (Malware, Ransomware, Phishing)
- Endpoint Protection Solutions (Antivirus, EDR, DLP)
- Hands-on: Configuring Endpoint Security Software & Conducting Malware Scans
Offensive Security (Ethical Hacking)
- Understanding Ethical Hacking & Pentesting Methodology
- Basics of Reconnaissance & Footprinting
- Common Exploits (SQL Injection, XSS, Buffer Overflow)
- Hands-on: Using Kali Linux for Basic Scanning (Nmap, Metasploit)
Defensive Security (Blue Teaming)
- Security Monitoring & Incident Detection (SIEM, Log Analysis)
- Security Policies & Compliance (ISO 27001, NIST)
- Incident Response Basics (SOC Operations)
- Hands-on: Setting Up a SIEM (e.g., Splunk, ELK) & Analysing Logs
Incident Response & Digital Forensics
- Incident Response Lifecycle (Preparation, Detection, Containment, Eradication, Recovery)
- Basics of Digital Forensics (File System Analysis, Memory Forensics)
- Hands-on: Capturing and Analysing Logs from a Cyber Incident
Malware Analysis & Reverse Engineering
- Types of Malwares & Their Behaviours
- Static & Dynamic Malware Analysis Techniques
- Basics of Reverse Engineering (Disassemblers, Debuggers)
- Hands-on: Analysing a Malware Sample in a Safe Lab Environment
Threat Intelligence & Cyber Threat Hunting
- Understanding Threat Intelligence (TTPs, Cyber Kill Chain, MITRE ATT&CK)
- Proactive Threat Hunting Techniques
- Threat Intelligence Sources & Tools (OSINT, VirusTotal, Threat Feeds)
- Hands-on: Conducting a Threat Hunt Using Open-Source Tools
Intermediate hands-on modules.
Vulnerability Management
Vulnerabilities are the weaknesses in our systems which hackers use to attack the system. We'll start this lesson by learning how to scan for vulnerabilities using automated tools. Then we will learn how to manage any found vulnerabilities in a central dashboard, prioritize them based on risk levels, and track response efforts and management decisions. We'll also learn how to manually calculate risk scores and assign risk ratings to the vulnerabilities. We'll conclude the lesson with a discussion of false positives and false negatives.
System Auditing
In this lesson, we will learn how to read a test scope document and start gathering information about our target system. We will learn how to research the vulnerabilities find their exploits and how to validate the vulnerabilities by executing an exploit. Then we'll learn how to prepare a report on our findings. We will end this lesson with a discussion about why some exploits are intentionally written with bugs.
Application Auditing
We will start learning about application auditing by looking at the OWASP Web Security Testing Guide and how it can be used in our testing. Next, we will learn how to send requests to a web application and analyse the response that comes back. We will use semi-automated tools to increase the efficiency and accuracy of our tests. We'll also use fully automated tools to perform specific tasks to create output we can use in further testing. Finally, we'll look at other systems and products that are vulnerable to hacking.
Social Engineering
In this lesson, we will take a look at the human side of Ethical Hacking. We will begin with a discussion of five opportunities in human psychology that hackers use to manipulate our employees. Then we will learn how to perform an enterprise-level phishing simulation and create malware. We will also learn how to create an effective landing page for social engineering attempts. We will wrap up our lesson with a discussion about the ethics of social engineering.
Open-Source Intelligence (OSINT)
We'll start gathering open-source intelligence by using Exploratory Link Analysis. Next, we'll learn how to do data mining. After we have gathered information, we will start grouping information and building links using a tool called Maltego. Then we will learn how to analyse the links and relationships we have established to create new information and draw conclusions based on the information we have uncovered. We will end the lesson with a brief discussion about using OSINT to uncover a hacker's identity.
Benefits of learning cybersecurity.
- Enhanced customer trust
- Computer security
- High salaries
- Rapid career growth
- Job security
- Protecting personal data
Essential security concepts.
The CIA Triad
Confidentiality protects data against unauthorized access. Integrity protects data and systems against unauthorized alteration. Availability protects data and systems against destruction or disruption of access. These are the most fundamental goals of security.
IAAA
Identification: a user must have an identity, like a username. Authentication: the user proves that identity, for example with a password. Authorization: the system checks access rights before granting access. Auditing: everything the user does is securely logged.
Choose your level.
₦250,000
- Network and endpoint security
- Ethical hacking and blue teaming
- Incident response and forensics
- Malware analysis and threat hunting
₦400,000
- Vulnerability management
- System and application auditing
- Social engineering
- Open-source intelligence (OSINT)
Before you apply.
What should I know before I start?
You should understand the essential security concepts in the Before you start section, the CIA Triad and IAAA. The Foundation course builds from there.
What is the difference between Foundation and Intermediate?
Foundation (2 months, ₦250,000) covers networks, endpoints, offensive and defensive security, incident response, malware analysis and threat intelligence. Intermediate (3 months, ₦400,000) is hands-on ethical hacking: vulnerability management, system and application auditing, social engineering and OSINT.
Do I get a certificate?
Yes. You receive a certificate of completion when you finish the course.
What time are classes?
Classes start from 10am. The exact schedule depends on the package you choose, and our admissions team will confirm it when you apply.
How do I apply and pay?
Complete the application form at the bottom of this page or message us on WhatsApp. Our payment terms and conditions are linked in the tuition card at the top of the page.
- Live, instructor-led classes from 10am
- Practical exercises and projects
- Certified, experienced trainers
- Hands-on labs and demonstrations
- Certificate of completion
Call +234 705 9999833
Start your journey.
More Courses
Explore More Courses
Analyse data and uncover insights with Python, SQL, visualisation and real datasets.
Learn Windows, Word, Excel, PowerPoint and the web in short, practical sessions.
Connect your everyday tools and let AI handle the repetitive busywork for you.
